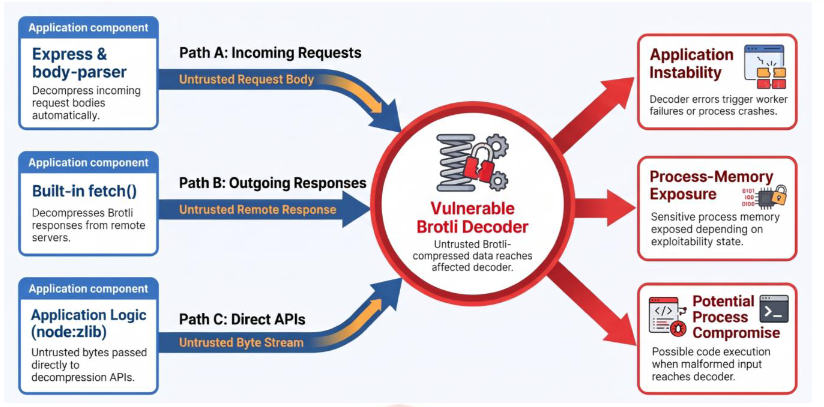
Node2Shell (CVE-2026-111497) Critical Brotli Decoder Vulnerability Under Active Exploitation
The vulnerability affects Node.js applications that use the vulnerable decoder and may also affect other software incorporating vulnerable Brotli impl....
29-Oct-2026 13:30:00
Read Details
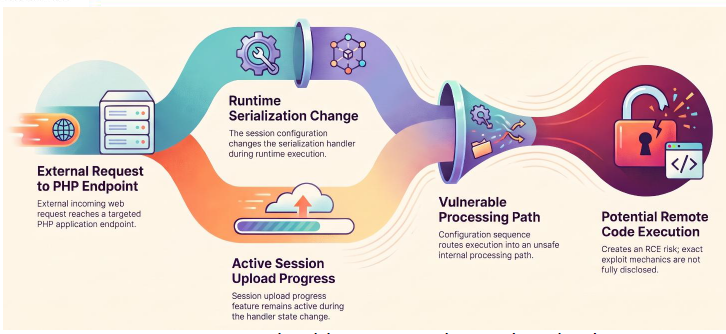
Unpatched PHP Remote Code Execution Vulnerability in Session Upload Progress CVE-2026-115560
BGD e-GOV CIRT alerts organizations to a newly disclosed PHP remote code execution vulnerability, tracked as CVE-2026-115560. The issue concerns an in....
27-Oct-2026 10:40:00
Read Details
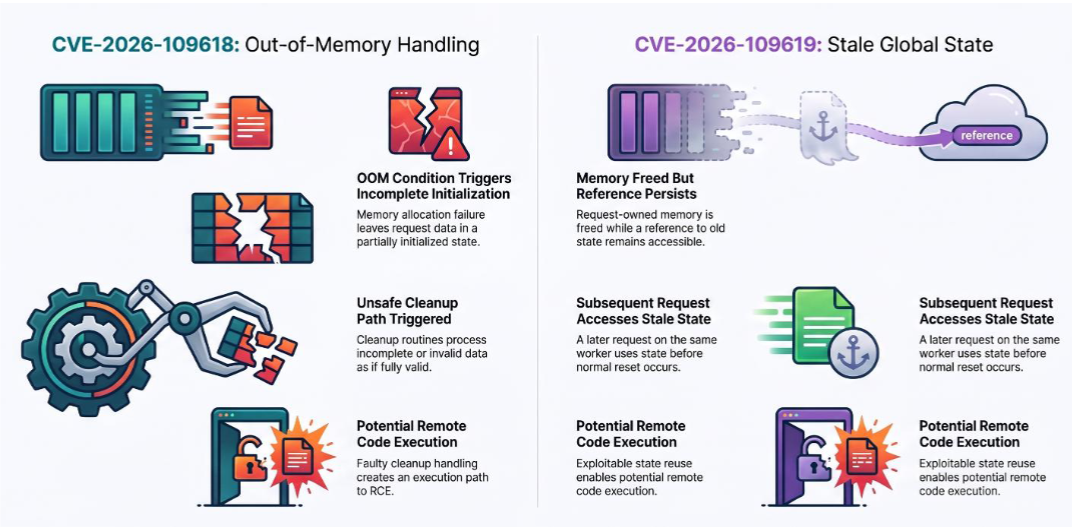
PHP2Shell: Critical Unauthenticated Remote Code Execution Vulnerabilities in PHP
The official security notice identifies PHP-FPM, Apache with mod_php, php-cgi, FrankenPHP and LiteSpeed deployments as potentially at risk. It highlig....
22-Oct-2026 11:00:00
Read Details
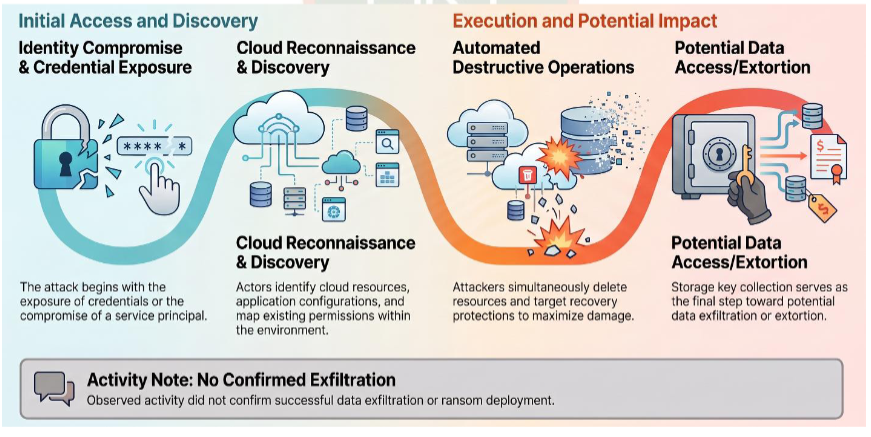
Agentic Driven Cloud Attack Using Compromised Service Principals
The investigated activity involved two compromised service principals. One primarily performed reconnaissance, while the second performed extensive di....
01-Oct-2026 12:00:00
Read Details
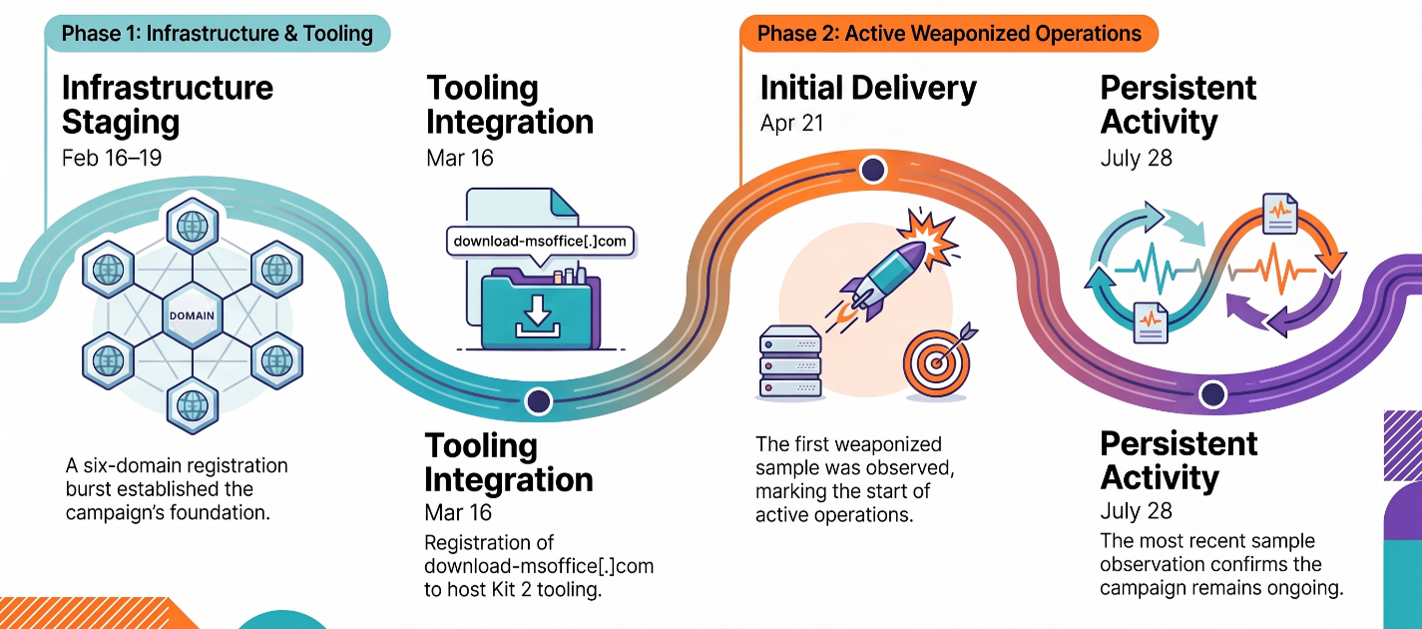
SideCopy Campaign Using MSHTA, Weaponized LNK and Fileless RAT Execution
BGD e-GOV CIRT has reviewed recent reporting on a SideCopy campaign employing spear- phishing, weaponized Windows shortcut (.LNK) files, mshta.exe, mu....
23-Sep-2026 14:30:00
Read Details
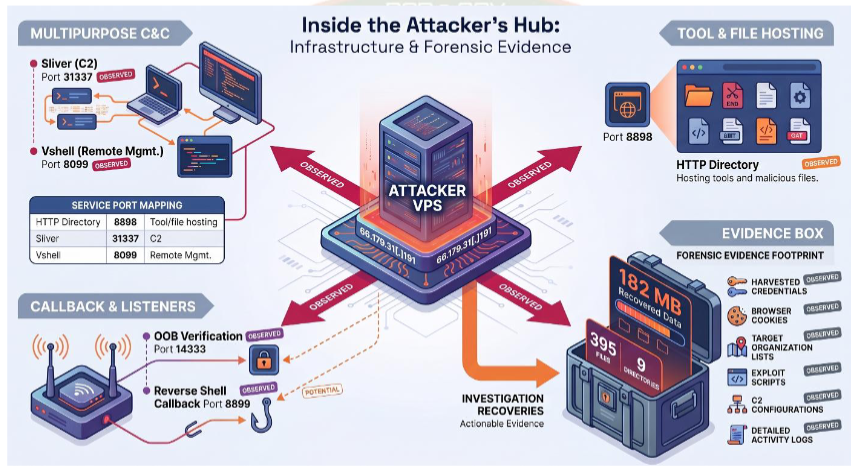
SideWinder-Associated Campaign Targeting South Asian Government and Financial Infrastructure
The recovered toolkit included exploitation capability against GeoServer/GeoTools, Laravel Ignition, Apache Tomcat Manager and Redis, as well as weak-....
17-Sep-2026 15:00:00
Read Details