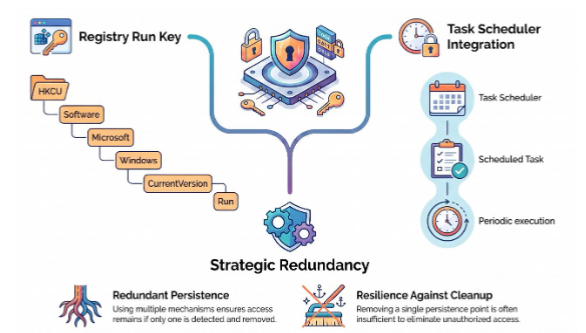
TerminalFix Campaign: ClickFix- Based Multistage Intrusion Deploying Reverse Tunneling and Active Directory Reconnaissance
This effectively turns the infected workstation into a proxy/pivot point inside the organization's trusted network. Microsoft specifically describes t....
02-Sep-2026 15:30:00
Read Details
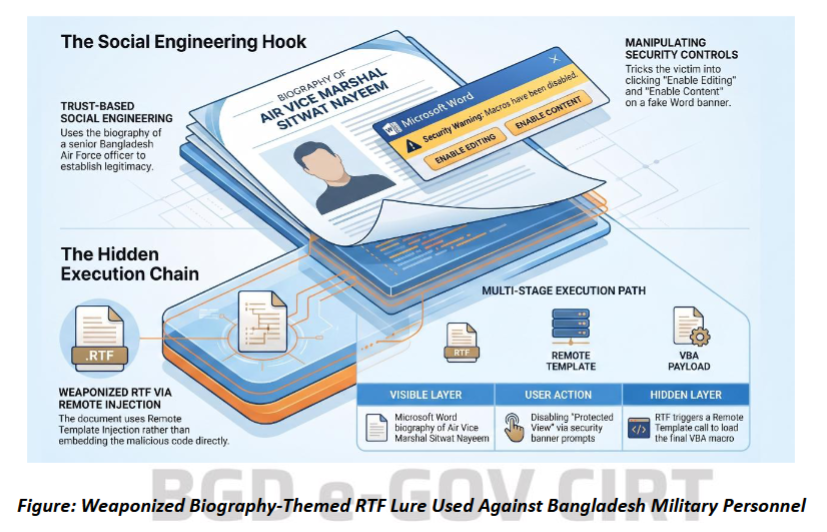
DoNot (APT-C-35) Cyber-Espionage Campaign Targeting Bangladesh Military and Defence Personnel
The lure itself was customized around Bangladesh’s military environment. The malicious document used the biography of a Bangladesh Air Force officer a....
17-Aug-2026 12:00:00
Read Details

The Gentlemen Ransomware: A Rapidly Scaling RaaS Threat Targeting Bangladesh
The group operates a cross-platform, self-propagating encryptor that can independently spread across Windows, Linux, NAS, BSD, and VMware ESXi systems....
09-Aug-2026 15:00:00
Read Details

SideWinder Spear-Phishing Campaign Against Bangladesh Leveraging Dual-Format Weaponized Documents
SideWinder, a persistent advanced persistent threat (APT) group with suspected India-nexus affiliations, is conducting an active spear-phishing campai....
30-Jul-2026 15:00:00
Read Details

GoldFactory / GoldPickaxe - Biometric-Stealing Mobile Banking Trojan Targeting e-KYC & Digital Identity Systems
The current variant is distributed via a malicious domain spoofing KuaiBo, a prominent Chinese video-streaming and media-player application. Fake webs....
21-Jul-2026 11:00:00
Read Details

Ghost Phishing: AES-GCM Encrypted Lures and EvilTokens Device-Code Phishing-as-a-Service Kit Targeting Microsoft 365 Accounts
The OAuth 2.0 Device Authorization Grant ("device code flow") is a legitimate authentication mechanism designed for devices with limited input capabil....
13-Jul-2026 15:15:00
Read Details